
Adding Credentials
For Sandfly to log in to a remote host, it must have a working SSH credential. Sandfly can use four SSH credential types:
- Username and password
- SSH private key and optional password
- Generated key
- External credential provider
Account Requirements
Sandfly needs an account with root-level privileges, because it examines areas of the operating system that normal users cannot access.
You can have Sandfly log in as root, but many systems do not allow this. Instead, set up an account that has sudo privileges for use by this application. Sandfly is able to log in and determine if it needs sudo to run. If so, it will use sudo, and if it has proper permissions, it will run normally.
Credentials Page
Selecting Asset management > Credentials in the sidebar menu will take you to the Credentials page.
All registered credentials will be displayed in the table. The table will be empty if no credentials have been created. To open the Add credential form, use the option to add a credential in the upper-right corner of the Credentials page.
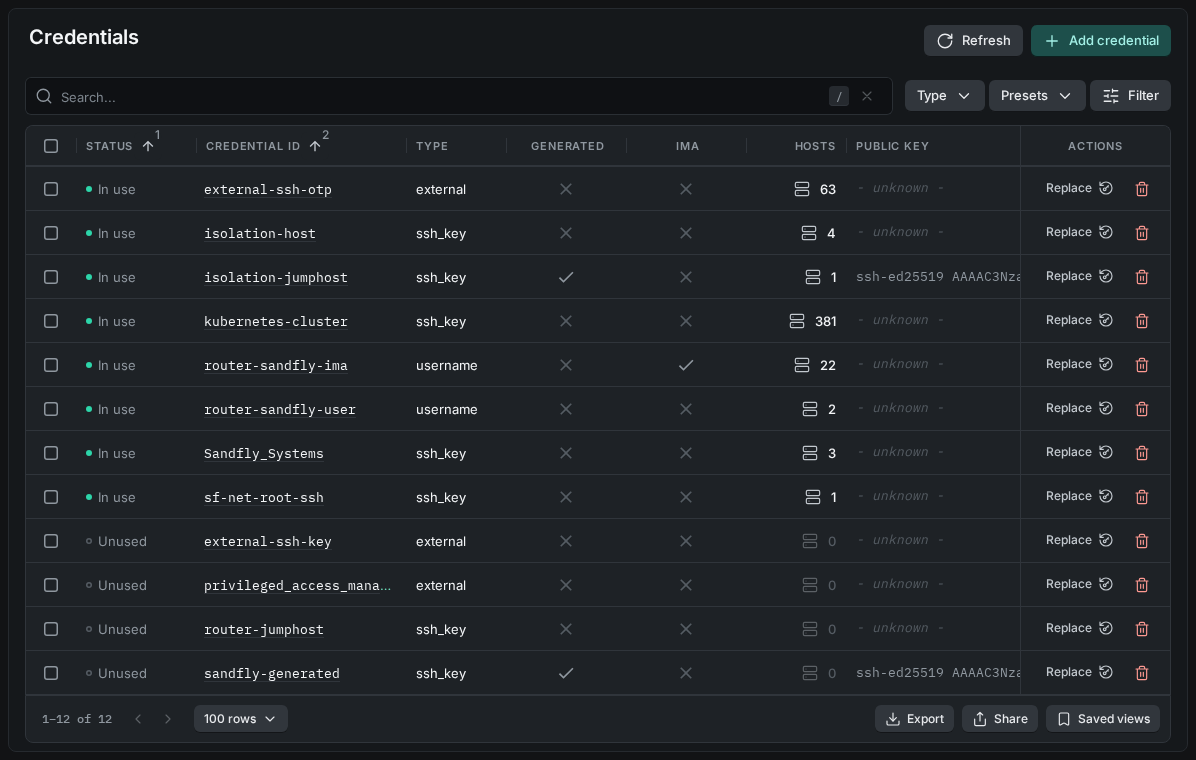
Credentials Page
Username and Password
IMPORTANT: Username and Password SSH Authentication is Dangerous!We do not recommend username/password SSH authentication unless you have no other options. If the remote system is compromised, logging in with a username and password allows the attacker to steal your credentials and use them elsewhere.
To protect against this risk, we only recommend you use SSH public key authentication as outlined in the next section.
If you want Sandfly to use a username/password, you can select that option in the form, shown below.
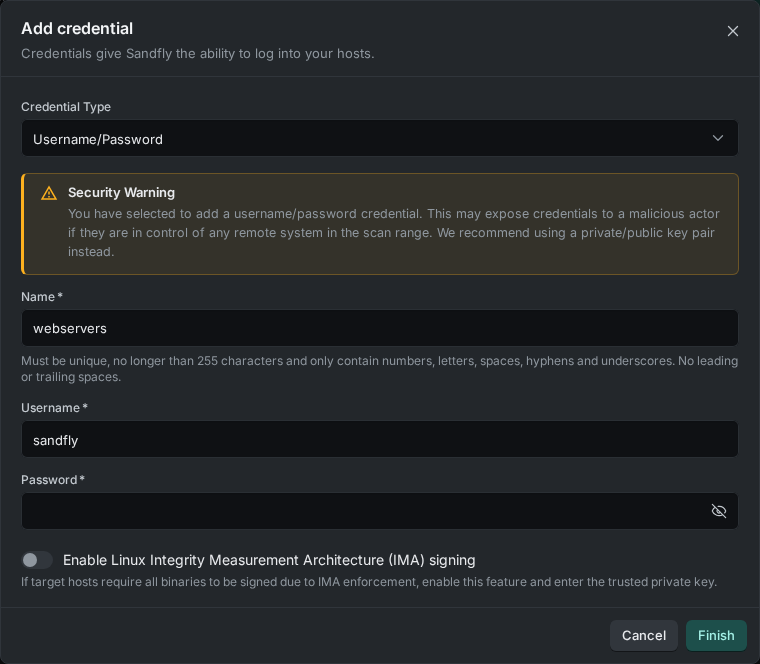
Adding a Username Credential
The fields in the above image mean the following:
Credential Type - Select the Username/Password option.
Name - A human-readable label that Sandfly uses to refer to this credential. For example, webservers could indicate that the credential is used to access web systems. This text field can only contain numbers, letters, spaces, hyphens, and underscore (_) characters.
CAUTION: Letters, Numbers, Spaces, Hyphens, And Underscore OnlyIn the credential Name field, you can only use uppercase and lowercase letters, numbers, spaces, hyphens (-), and the underscore (_). Do not start or end the name with a space. The name must be unique and no longer than 255 characters.
Username - The username you want Sandfly to use to log in to the remote host. This must be a legal Linux username.
Password - The password to use for this user. This also assumes that the same password is used for sudo access if needed.
IMPORTANT: Sudo Password Should Match User PasswordSandfly assumes the user's login password will also be the sudo password if needed. If no sudo password is needed by this user, Sandfly will figure that out and not use it.
After you enter these values, submit the form. Sandfly encrypts and stores the credential. After you add a credential, you cannot read it again.
SSH Private Key and SSH Certificates
The process for adding an external SSH private key is largely identical to that for usernames and passwords. You can use a basic SSH private key, or use a private key and SSH certificate. Optionally, if the key is encrypted, you can enter the decryption password as well.
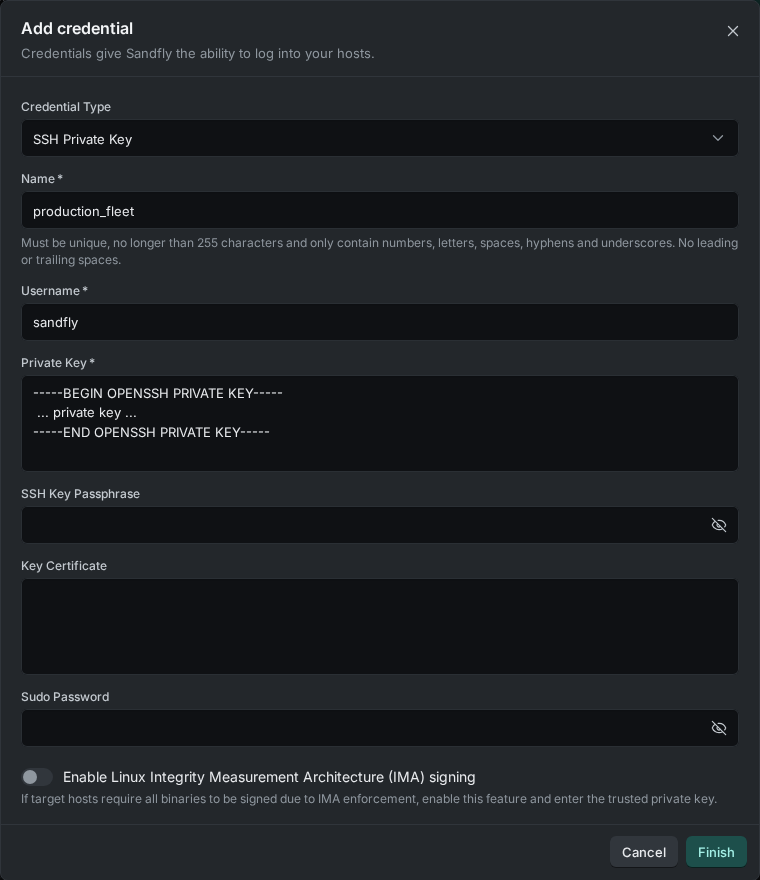
Adding an External SSH Credential
The fields in the above image mean the following:
Credential Type - Select the SSH Private Key option.
Name - A human-readable label that Sandfly uses to refer to this credential. For example, production_fleet could indicate that the credential is used to access production systems. This text field can only contain numbers, letters, spaces, hyphens, and underscore (_) characters.
CAUTION: Letters, Numbers, Spaces, Hyphens, And Underscore OnlyIn the credential Name field, you can only use uppercase and lowercase letters, numbers, spaces, hyphens (-), and the underscore (_). Do not start or end the name with a space. The name must be unique and no longer than 255 characters.
Username - The username you want Sandfly to use to log in to the remote host. This must be a legal Linux username.
Private Key - The SSH private key in standard SSH key export format.
SSH Key Passphrase (optional) - The password used to decrypt the SSH private key if one was used.
Key Certificate (optional) - The SSH certificate that matches the private key as signed by your SSH Certificate Authority (CA). We recommend that you use an SSH CA where possible.
Sudo Password (optional) - The sudo password for this user if one is needed. If supplied, Sandfly will use this password to obtain root privileges.
Again, after you enter these values, submit the form. Sandfly encrypts and stores the credential. After you add a credential, you cannot read it again.
Generate SSH Key
An SSH key can be generated via the user interface for use as a credential. Three SSH key types are currently supported:
- ed25519
- RSA 4096 bits
- RSA 8192 bits
The process for adding a generated key is largely identical to that for the username / password option.
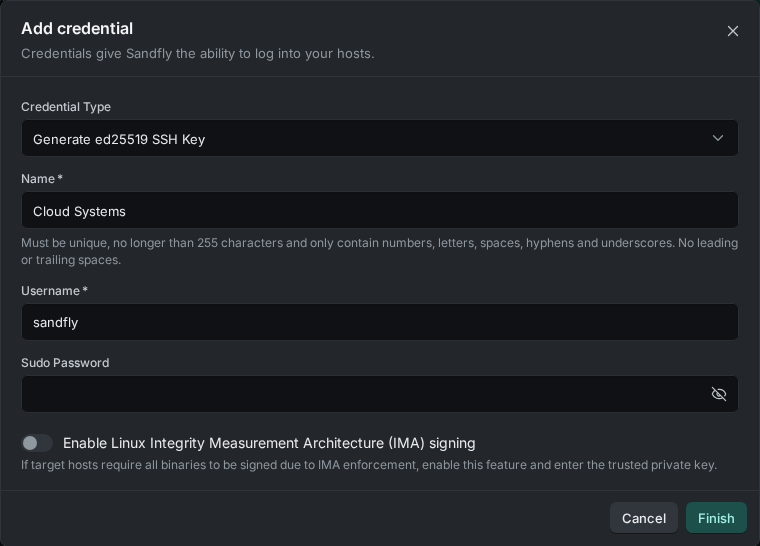
Adding a Generated SSH Credential
The fields in the above image mean the following:
Credential Type - Select your preferred SSH key type from one of the Generate options.
Name - A human-readable label that Sandfly uses to refer to this credential. For example, Cloud Systems could indicate that the credential is used to access cloud-based hosts. This text field can only contain numbers, letters, spaces, hyphens, and underscore (_) characters.
CAUTION: Letters, Numbers, Spaces, Hyphens, And Underscore OnlyIn the credential Name field, you can only use uppercase and lowercase letters, numbers, spaces, hyphens (-), and the underscore (_). Do not start or end the name with a space. The name must be unique and no longer than 255 characters.
Username - The username you want Sandfly to use to log in to the remote host. This must be a legal Linux username.
Sudo Password (optional) - The sudo password for this user if one is needed. If supplied, Sandfly will use this password to obtain root privileges.
Again, after you enter these values, submit the form. Sandfly encrypts and stores the credential. After you add a credential, you cannot read it again.
For a generated key, and for an SSH private key credential, the public key shows in the Public Key column of the Credentials page and on the Public Key card of the credential's Details page. To copy it, click Copy on the card, or click the copy icon that shows when you hover over the column value.
External Credential Provider
The steps for adding an external credential provider involve the completion of the form. The following fields are provided:
Credential Type - Select the External Credential Provider option.
Name - A human-readable label that Sandfly uses to refer to this credential. For example, production_fleet could indicate that the credential is used to access production systems. This text field can only contain numbers, letters, spaces, hyphens, and underscore (_) characters.
CAUTION: Letters, Numbers, Spaces, Hyphens, And Underscore OnlyIn the credential Name field, you can only use uppercase and lowercase letters, numbers, spaces, hyphens (-), and the underscore (_). Do not start or end the name with a space. The name must be unique and no longer than 255 characters.
URL of external credential adapter service - The URL of the service. It must start with http:// or https://.
Make unique credential request per host - When turned on, Sandfly makes a separate credential request to the external service for each host, and the request includes the address and SSH port of the target host.
External credential service extra data (optional) - Provide any additional options that may be needed for the external service.
External credential service root CA certificate (optional) - The root CA certificate for the external service.
Again, after filling in the necessary fields, submit the form to save the credential.
Refer to the External Credential Provider Interface documentation for full details about this option.
Integrity Measurement Architecture (IMA) Signing
Some systems (e.g., Juniper's Junos OS Evolved routers) have IMA, the Linux Integrity Measurement Architecture, enabled. This requires that all binaries and libraries on a machine are signed with a key from the trusted keystore. Sandfly can add the signature to the agent binary when Sandfly pushes it to the remote system.
If you have hosts that require IMA, turn on Enable Linux Integrity Measurement Architecture (IMA) signing, and then paste the signing key into the IMA Signing Key field. The key must be a PEM-encoded RSA private key in PKCS#1 or PKCS#8 format. If the key is an encrypted PKCS#8 key, also enter its password in the IMA Signing Key Password field.
We recommend that you create dedicated credentials in Sandfly for the hosts that need IMA signing.
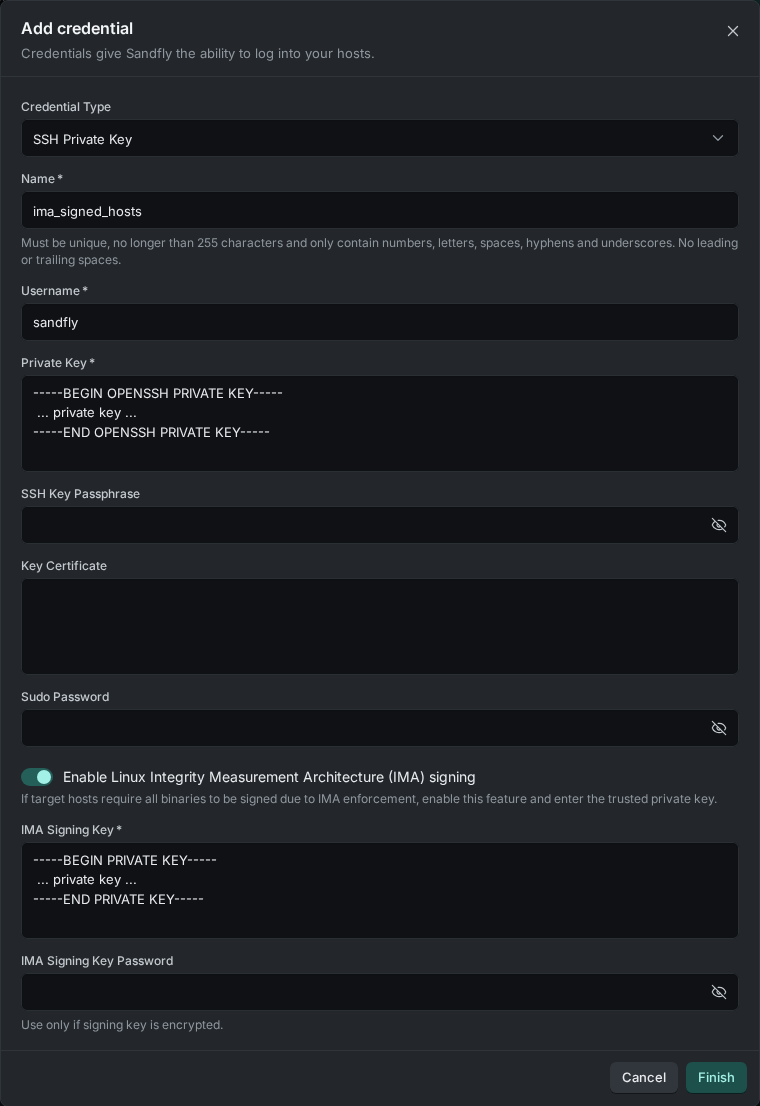
Credential - Integrity Measurement Architecture (IMA) Signing
Auto-Protection
When you add or replace a credential that uses an SSH private key or a generated SSH key, Sandfly automatically adds its public key to SSH Investigation and sets it as a Protected key. When you replace or delete a credential, its old public key stays Protected in SSH Investigation until you unprotect it. SSH keys of credentials added to Sandfly prior to version 5.8.0 must be manually protected. See the Key Protection section of the SSH Key Response Actions documentation for more information about protected keys.
Updated about 20 hours ago