
Audit Log
The audit log records application-level activity in Sandfly. To open the audit log, in the sidebar menu, select Logs > Audit log.
Users with the admin or power_user role can view the audit log. Only users with the admin role can clear the audit log.
Each entry has these columns:
- Time - The date and time of the event.
- Type - The record type:
security- An event from a user or API request.system- An event that Sandfly starts internally.error- A request that failed with an internal server error.
- Username - The Sandfly user that caused the event. System events show
[system]. Events without an authenticated user show[unknown]. - Message - The event message. The column shows truncated text.
- IP Address - The source IP address of the request. System events show
0.0.0.0. - Id - The ID of the entry. This column is hidden by default.
To see the full entry, click the expand button at the start of the row. The expanded row shows the username, the source IP address, the timestamp, the record type, and the full message text.
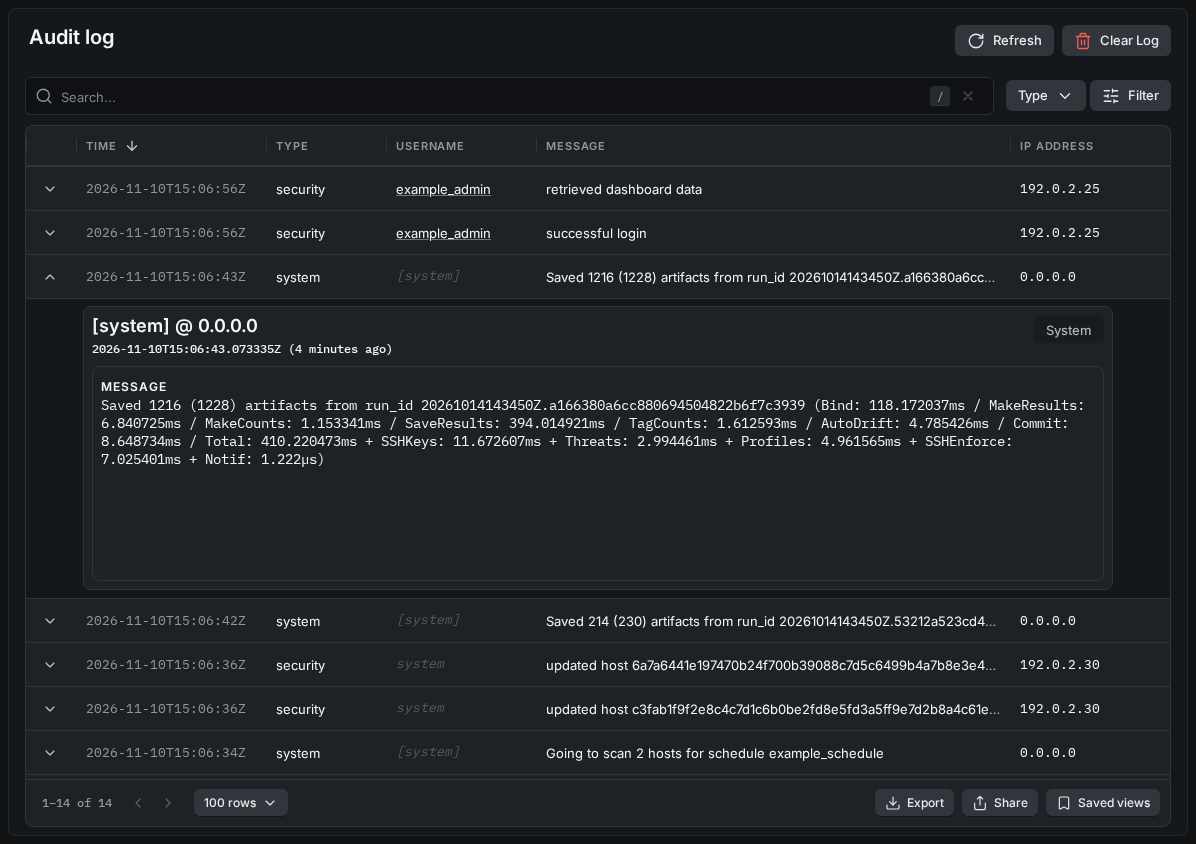
Expanded Audit Log Entry
Sandfly automatically deletes audit log entries that are older than the Data retention value. To see or change this value, in the sidebar menu, select Settings > Application settings > General, and then go to the Server and data retention card.
Clear Audit Log
Clear the audit log to delete all of its entries.
CAUTION: You cannot undo a clear of the audit logClearing the audit log permanently deletes all entries. You cannot recover the deleted entries.
- In the sidebar menu, select Logs > Audit log.
- In the upper-right corner of the page, click Clear Log.
- In the Warning dialog, click Proceed. To stop, cancel the dialog.
After the clear, the oldest entry in the log is cleared audit log, with your username. The log shows the newest entries first, so this entry is at the bottom of the list.
Updated 8 days ago