
Syslog
Located under Settings > Integrations > Syslog, the Syslog tab enables the configuration of result and log data forwarding to an external syslog receiver for independent, long-term storage and data analysis.
INFO: Upgrade Feature - SyslogThe ability to configure and use Syslog requires an upgraded plan. Please see https://www.sandflysecurity.com/get-sandfly/🡵 for details.
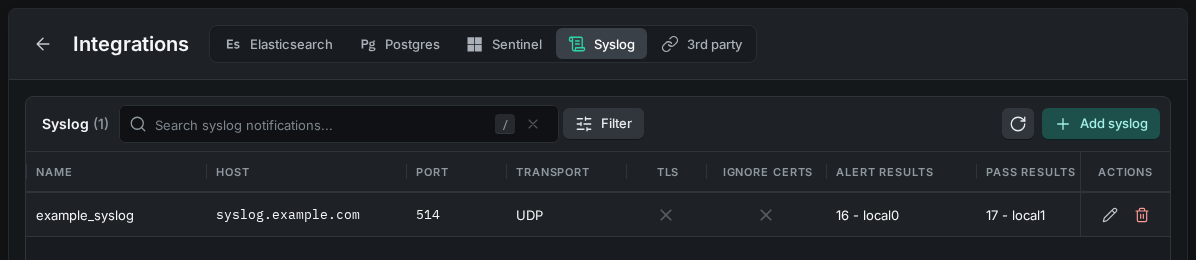
Syslog Tab
The Syslog tab lists the configured syslog servers with their name, host, port, transport, TLS setting, facilities, and replication options. Use the row actions to edit an entry, or to delete it after you confirm the deletion in the confirmation dialog.
Rich Structured Data
The syslog alerts Sandfly sends are rich structured data. With Full JSON Results selected, Sandfly sends the complete result, as shown in the Sandfly UI. Therefore, you can set up Sandfly to monitor your hosts, and use your existing monitoring tools to view alerts without needing to use the Sandfly UI.
Furthermore, the data Sandfly sends contains extended attributes that allow you to search across a variety of keywords about the data, status of the alert, alert type and other key metadata.
TIP: Generate Test Alerts To See Syslog OutputOnce you set Sandfly up to send syslog output, it may be useful to generate some alerts so that Sandfly can send them to your syslog server to make sure it is working.
If you want to do a quick test, go onto a host and run the following command:
mkdir /tmp/...This will make a suspicious directory under
/tmpcalled....When you run Sandfly against this host, you will see an alert activation for a suspicious directory under
/tmp. This alert will be sent to your syslog server if you set it up correctly.After you see this alert, be sure to do a
rmdir /tmp/...to get rid of the directory or you will get repeated alerts from Sandfly about the suspicious entry.
Add Syslog Integration Form
To add a syslog server, use the option to add one in the table toolbar. The form contains the following configurable fields:
-
Name - A unique name for the syslog server, 255 characters maximum. Use only letters, numbers, spaces, hyphens, and underscores. You cannot change the name after you save the entry.
-
Hostname - Hostname or IP address of the syslog server.
-
Transport - Select which transport method to use; options include UDP and TCP. The default is UDP.
When you select TCP, the Use TLS option becomes available. When you turn on Use TLS, these additional fields become available:
- Use TLS - Turn on to create an encrypted connection to the syslog server.
- Ignore Certificate Validation Errors - Turn on to allow connections to the syslog server even if the server certificate fails validation. When this option is on, Sandfly ignores the Trusted CA Certificate(s) field.
- Trusted CA Certificate(s) - Sandfly will trust certificates from public certificate authorities by default. If your syslog server uses a certificate from a private CA or is self-signed, provide the trusted certificate in PEM format in this field.
-
Port - The port of the syslog server. Enter a port from 1 to 65535. The default is 514, the standard syslog port, for all transports.
Syslog Entries to Send
Sandfly can send Alert results, Pass results, Audit Log entries, and Scan Error Log entries to syslog. In this section of the form, select the types of data and the syslog facility you would like Sandfly to send to this syslog server.
- Alert Results Facility - Select or disable the syslog facility used for outgoing alert results.
- Pass Results Facility - Select or disable the syslog facility used for outgoing pass results.
- Audit Log Entries Facility - Select or disable the syslog facility used for outgoing audit log entries.
- Scan Error Log Entries Facility - Select or disable the syslog facility used for outgoing scan error log entries.
Each facility defaults to Disabled. To send that entry type, select a facility (0-23). Sandfly sends error results only when both Alert Results Facility and Pass Results Facility are set. Error results use the alert results facility.
Replication Options
Replication options apply only when Alert Results Facility or Pass Results Facility is set to a facility.
- Full JSON Results (optional) - Enable to send the complete result JSON, including host and sandfly details, with no message size limit. This option overrides the summary options and requires the TCP transport. This option is not available with UDP. When you select it, Sandfly clears and disables Summary Results and Summary Duplicate Alerts. Without this option, Sandfly sends only the result data, and it shortens this data to approximately 64,000 bytes.
- Summary Results (optional) - Enable to include just the explanation text rather than the full JSON data. Note that the explanation text only explains the alert and does not include the details in the full JSON data. This setting applies to all alert, pass, and error results that Sandfly sends, including resolved alerts that Sandfly sends again, but not to duplicate alerts.
- Duplicate Alerts (optional) - Enable to send duplicate alerts when the alert last seen time is updated. Note: this only applies to Alerts and not Pass results. The last seen time is updated when an existing alert is triggered and updated with new information. This will result in a larger volume of data since the alert may be triggered each time a scan is performed on the target system.
- Summary Duplicate Alerts (optional) - Enable to include just the explanation text for duplicate alerts rather than the full JSON data. Note that the explanation text only explains the alert and does not include the details in the full JSON data. This setting only applies to duplicate Alerts and does not affect new Alerts or new Pass results. This option is available only when Duplicate Alerts is on and Full JSON Results is off.
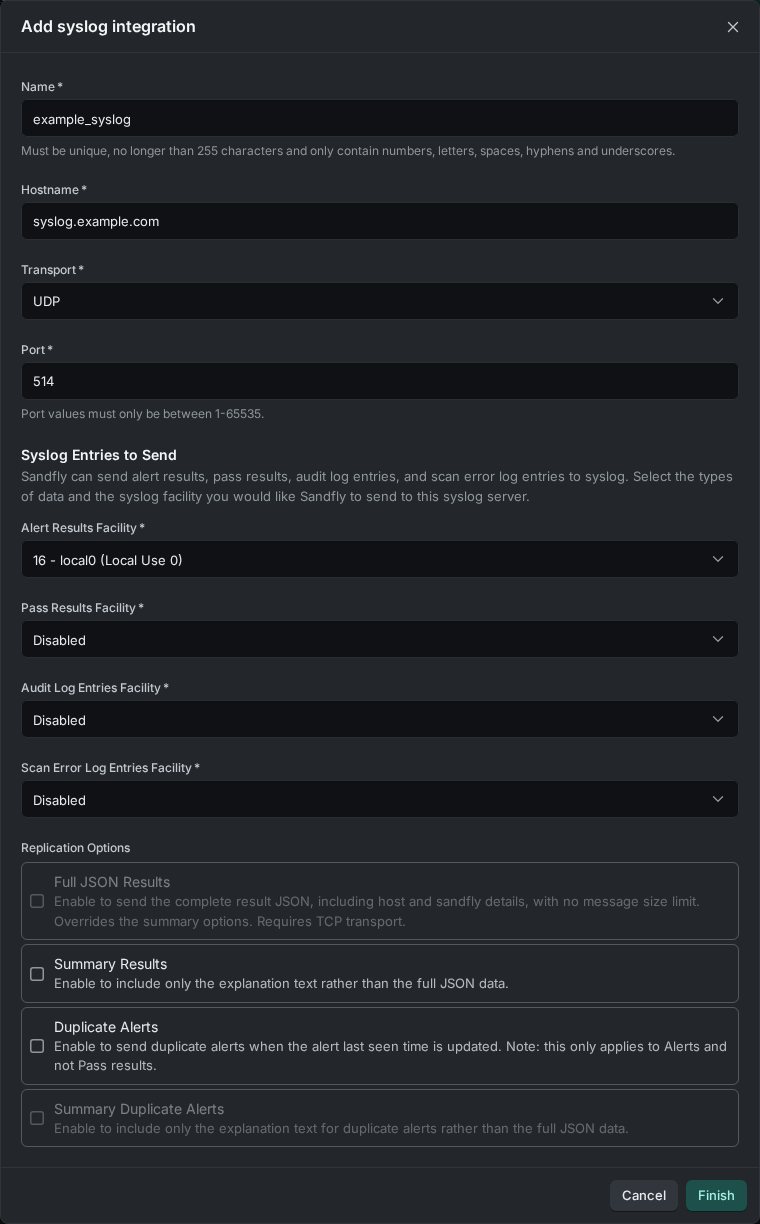
Add Syslog Integration Form
Once the form is completed, submit it to save and activate the syslog entry.
IMPORTANT: Allow Appropriate Syslog Port AccessMake sure that the packet filter on your syslog server allows traffic from the Sandfly Server on the configured Port, with the protocol set in Transport (TCP or UDP). If the packet filter blocks this traffic, the syslog server does not receive the data.
Syslog Message Priority (PRI)
Facility
- Sandfly uses the facility that is set for the entry type. Error results use the alert results facility.
Severity
err("Error", numerical code 3) for Sandfly Alert results, error-level Audit Log entries, and Scan Error Log entries.warn("Warning", numerical code 4) for Sandfly Error results and warning-level Audit Log entries.info("Informational", numerical code 6) for Sandfly Pass results, informational-level Audit Log entries, and alerts that were resolved after Sandfly sent them (sent to the pass results facility).
Updated about 4 hours ago