
Triage Host Detail
When one host needs a closer look, open its Details page on the Triage tab. The tab lists every alerting artifact on the host, stacked by kind and sorted worst first, with the AI triage verdict and a preview of each detection beside it. This is where you decide whether the host has one incident or several, which detections are the incident, and what to do about them.
Opening a Host
Any of these opens the host's Details page:
- On the Host triage page, click Triage host on the Host triage summary card, or double-click the row. See Triage Hosts.
- On the Dashboard, click a host in the Top alerting hosts panel. It opens on the Triage tab.
- Anywhere a hostname is a link, such as the Artifacts list or an artifact's Details page.
- On the Hosts page (Asset management > Hosts), click the linked hostname or double-click the row.
When the host has alerting artifacts, the page header shows a Threats detected notice with the host's severity, the number of detections, and when the host was last seen. Click Investigate in the notice to go to the Triage tab. A host with results and nothing alerting shows No threats detected instead.
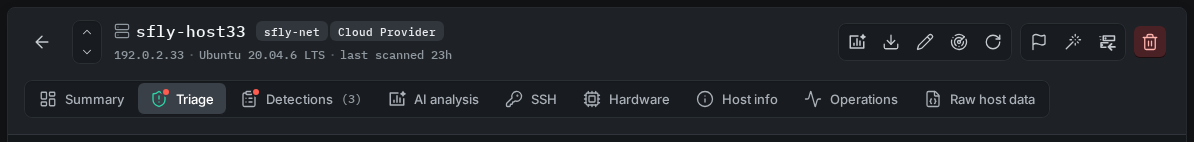
Host Details Page Header
The Tabs
The tabs of the Details page divide the host's data. For triage, you use mainly the first two, and the others for context:
- Summary - A rolled-up overview. The Host triage summary card is docked on the right, with the host's status dots, the AI triage verdict, and the Top detections; its View triage button opens the Triage tab. The Artifacts card counts the alerting artifacts by kind, and the AI Analysis card starts or shows an AI analysis of the host.
- Triage - The work surface described on this page and in Host Triage.
- Detections - The same alerting artifacts as a plain table, with every column, filtering, and export. Use it when you need to sort or filter by something other than severity.
- AI analysis - The AI analyses of this host, in the AI analysis workspace.
- SSH - The host's SSH keys, users, and zone violations; the same view as SSH investigation > SSH hosts.
- Hardware - CPU, memory, DMI data, mounts, and network interfaces.
- Host info - Recon data: processes, services, users, scheduled tasks, kernel modules, and more. This is the context that puts a detection in its place.
- Operations - Scan history, schedules, and other operational data.
- Raw host data - The host record as JSON.
Header Actions
The header has the actions that apply to the host as a whole: AI analysis, Download (the host JSON), Edit, Scan, Refresh, Flag host or Clear flag, Create drift profile (opens the Drift Detection Wizard), Add to drift profile, and Delete host.
The Triage Tab
The Triage tab stacks the host's alerting artifacts by kind, worst first, with the Artifact triage summary card beside them for the selected detection. Its groups, columns, card, and actions are described in Host Triage. In short: the group headers are colored by their worst member and stack worst first; empty groups are collapsed with a zero; the Finding column shows the AI classifier's verdict, the ML score, and the number of alerting sandflies; and a selection arms Whitelist, Respond, Add to profile, and Delete.
AI Triage on a Host
The AI triage block on the Host triage summary card (on the Summary tab) shows the host's verdict, if there is one. Use it as a starting point: the brief and the tags often name the incident before you open a single detection, and the findings tell you which detections the model grouped together. If the verdict is Stale, the host's alerts changed after it was formed; click Re-evaluate before you rely on it. For the states, the buttons, and what a verdict changes, see AI Triage.
Procedure
Step 1: Read the Host as a Whole
- Read the Threats detected notice: the severity, the number of detections, and when the host was last seen. Old evidence on a host that is scanned hourly is a sign that scans are failing.
- On the Summary tab, read the AI triage verdict and brief on the Host triage summary card, if there is one. Note the tags.
- Read the Artifacts card. Which kinds are alerting?
Step 2: Walk the Groups
- On the Triage tab, start with the top group and the top row.
- For each row, read Sev, Tags, and Finding. A
MLS 9xon a process or file is a strong signal on its own. - Click the row and read the Top results on the card. The explanation of each sandfly says exactly what it matched: a process running from a temporary directory, a file with the wrong owner, a user with no password, a cron entry that downloads something.
Step 3: Find the Incident
Attackers leave more than one trace. Look across the groups for detections that belong together:
| Pattern | Example |
|---|---|
| Execution plus staging | A process in Processes whose binary is in /tmp, /dev/shm, or /var/tmp, and the same path in Files. |
| Execution plus persistence | A suspicious process, and a Scheduled Tasks entry or a service that starts it again. |
| Hiding | A process that is hidden from ps, a binary that was deleted while the process runs, or a Kernel Modules entry that is not signed. |
| Access plus persistence | A new or changed user in Users, and a new SSH key on the SSH tab. |
| Cleanup | Missing or truncated logs in Logs, on a host with any of the above. |
A set of detections that fit one pattern is one incident. Judge it as one. A single SEV 2 detection that fits no pattern and is present on many hosts is probably noise.
Step 4: Use the Host Context
Open the Host info tab to place a detection in its context:
- Processes - Is the suspicious process a child of a web server, a cron job, or a user's shell? What is it connected to?
- Users - Does the account that owns the artifact exist for a reason? When was it created?
- Scheduled tasks and Services - Does anything start the artifact again after a reboot?
- Kernel modules - Is there a module that is not from the distribution?
Open the SSH tab for keys and zone violations, and the Operations tab for the scan history. A host whose scans started failing at the same time as the first detection deserves a direct look.
Step 5: Act
| Your conclusion | Do this |
|---|---|
| False positive | Whitelist the detections. Use the group's Whitelist all for a kind, or select the rows and click Whitelist. Use the Whitelist dialog to set the scope and the strictness. |
| Weakness to fix | Fix it on the host, then scan the host again. Do not whitelist a weakness; it is not a false positive. |
| Suspicious, need more | Click Triage artifact on the worst detection and continue with Triage Artifact Detail. Or click Pass to AI analysis for a written report. |
| Intrusion in progress | With the Responder role, select the processes and use Respond > Suspend processes to freeze them while you preserve evidence, and Retrieve binaries and files to pull the binary for analysis. Then isolate the host by your incident response procedure. |
| Confirmed compromise | Isolate the host. Keep the evidence. Do not delete the artifacts. See Result Response Actions for what each action does. |
CAUTION: Suspend Before You KillKilling a process destroys its memory, and with it the evidence of what it was doing. Suspending a process stops it from doing more harm while its memory, its open files, and its network connections stay available for analysis. Unless you are sure that a process must be stopped now, suspend it first.
Step 6: Confirm
- Click Scan in the header to scan the host again, or wait for the next scheduled scan.
- Open the Triage tab again. Detections that a newer scan no longer sees are superseded and leave the tab; the Detections tab still lists them, marked as not still seen.
- If the detections are gone because you fixed or whitelisted them, close the case. If they are gone and you changed nothing, treat it as a cleanup by someone else.
- Clear the flag if you set one.
Examples
One Incident, Three Groups
The host reads SEV 5, Likely compromised, High confidence, with tags cryptominer and persistence. The Processes group has a process kworkerds running from /tmp/.x/ with MLS 97 · 3 alerts, and its Top results say that the binary on disk was deleted and the process has an outbound connection to a mining pool. The Scheduled Tasks group has a cron entry for the same path. The Files group has the dropper script.
This is one incident. Suspend the process, retrieve the binary, and isolate the host. Whitelist nothing. After the host is rebuilt, delete it from Sandfly or scan it again to confirm that it is clean.
A Vendor Agent on a Build Server
The host reads SEV 4 with Likely false positive. The Processes group has a single process with MLS 62 · 2 alerts. The Top results say that the process is a binary that is not from a package and that it listens on a port. The AI brief names it as the backup agent that the host's tag says it should have, and the Host matches on the artifact's Details page show it on every host with the same tag.
Confirm the path and the publisher once, then whitelist the artifact with the Whitelist dialog scoped to Hosts by tag. The hosts drop out of High priority.
A Weak Password
The host reads SEV 3 with Needs attention. The Users group has the user deploy with the tag weak-password, and nothing else is alerting. The SSH tab shows no keys for that user, and the Host info tab shows no recent login.
Do not whitelist it. Have the password changed, scan the host again, and confirm that the detection is superseded.
Tips
- The Detections tab is the table view - When the groups get in the way, for example to sort by Last seen or to export, switch to Detections. Both tabs show the same artifacts.
- Group colors are a map - Before you read any row, the colors of the group headers tell you which kinds of artifacts carry the worst findings.
- Re-evaluate after you act - After a whitelist or a fix, click Re-evaluate so that the AI verdict and the host's severity reflect what is left.
- Errors are detections too - The Errors group lists sandflies that could not complete. A sandfly that times out on one host only may be a sandfly that something on the host is interfering with.
Updated about 2 hours ago